Understanding Two-Factor Authentication Versus Two-Step Verification: Clarifying the Key Differences
In today’s digital landscape, securing online accounts has become more critical than ever. Many users encounter terms like “Two-Factor Authentication” (2FA) and “Two-Step Verification” (2SV) when enhancing their account security. Although these phrases are often used interchangeably, understanding the subtle differences—and whether they are truly distinct—is essential for making informed security choices.
What Are Two-Factor Authentication (2FA) and Two-Step Verification (2SV)?
At a glance, both mechanisms serve the primary purpose of adding an extra layer of security to your login process. They aim to verify your identity by requiring an additional piece of information beyond just a username and password. However, the terminology and implementation details can vary depending on the website or service.
Two-Factor Authentication (2FA)
Two-factor authentication involves requiring two separate types of evidence—factors—before granting access:
- Something you know: A password or PIN.
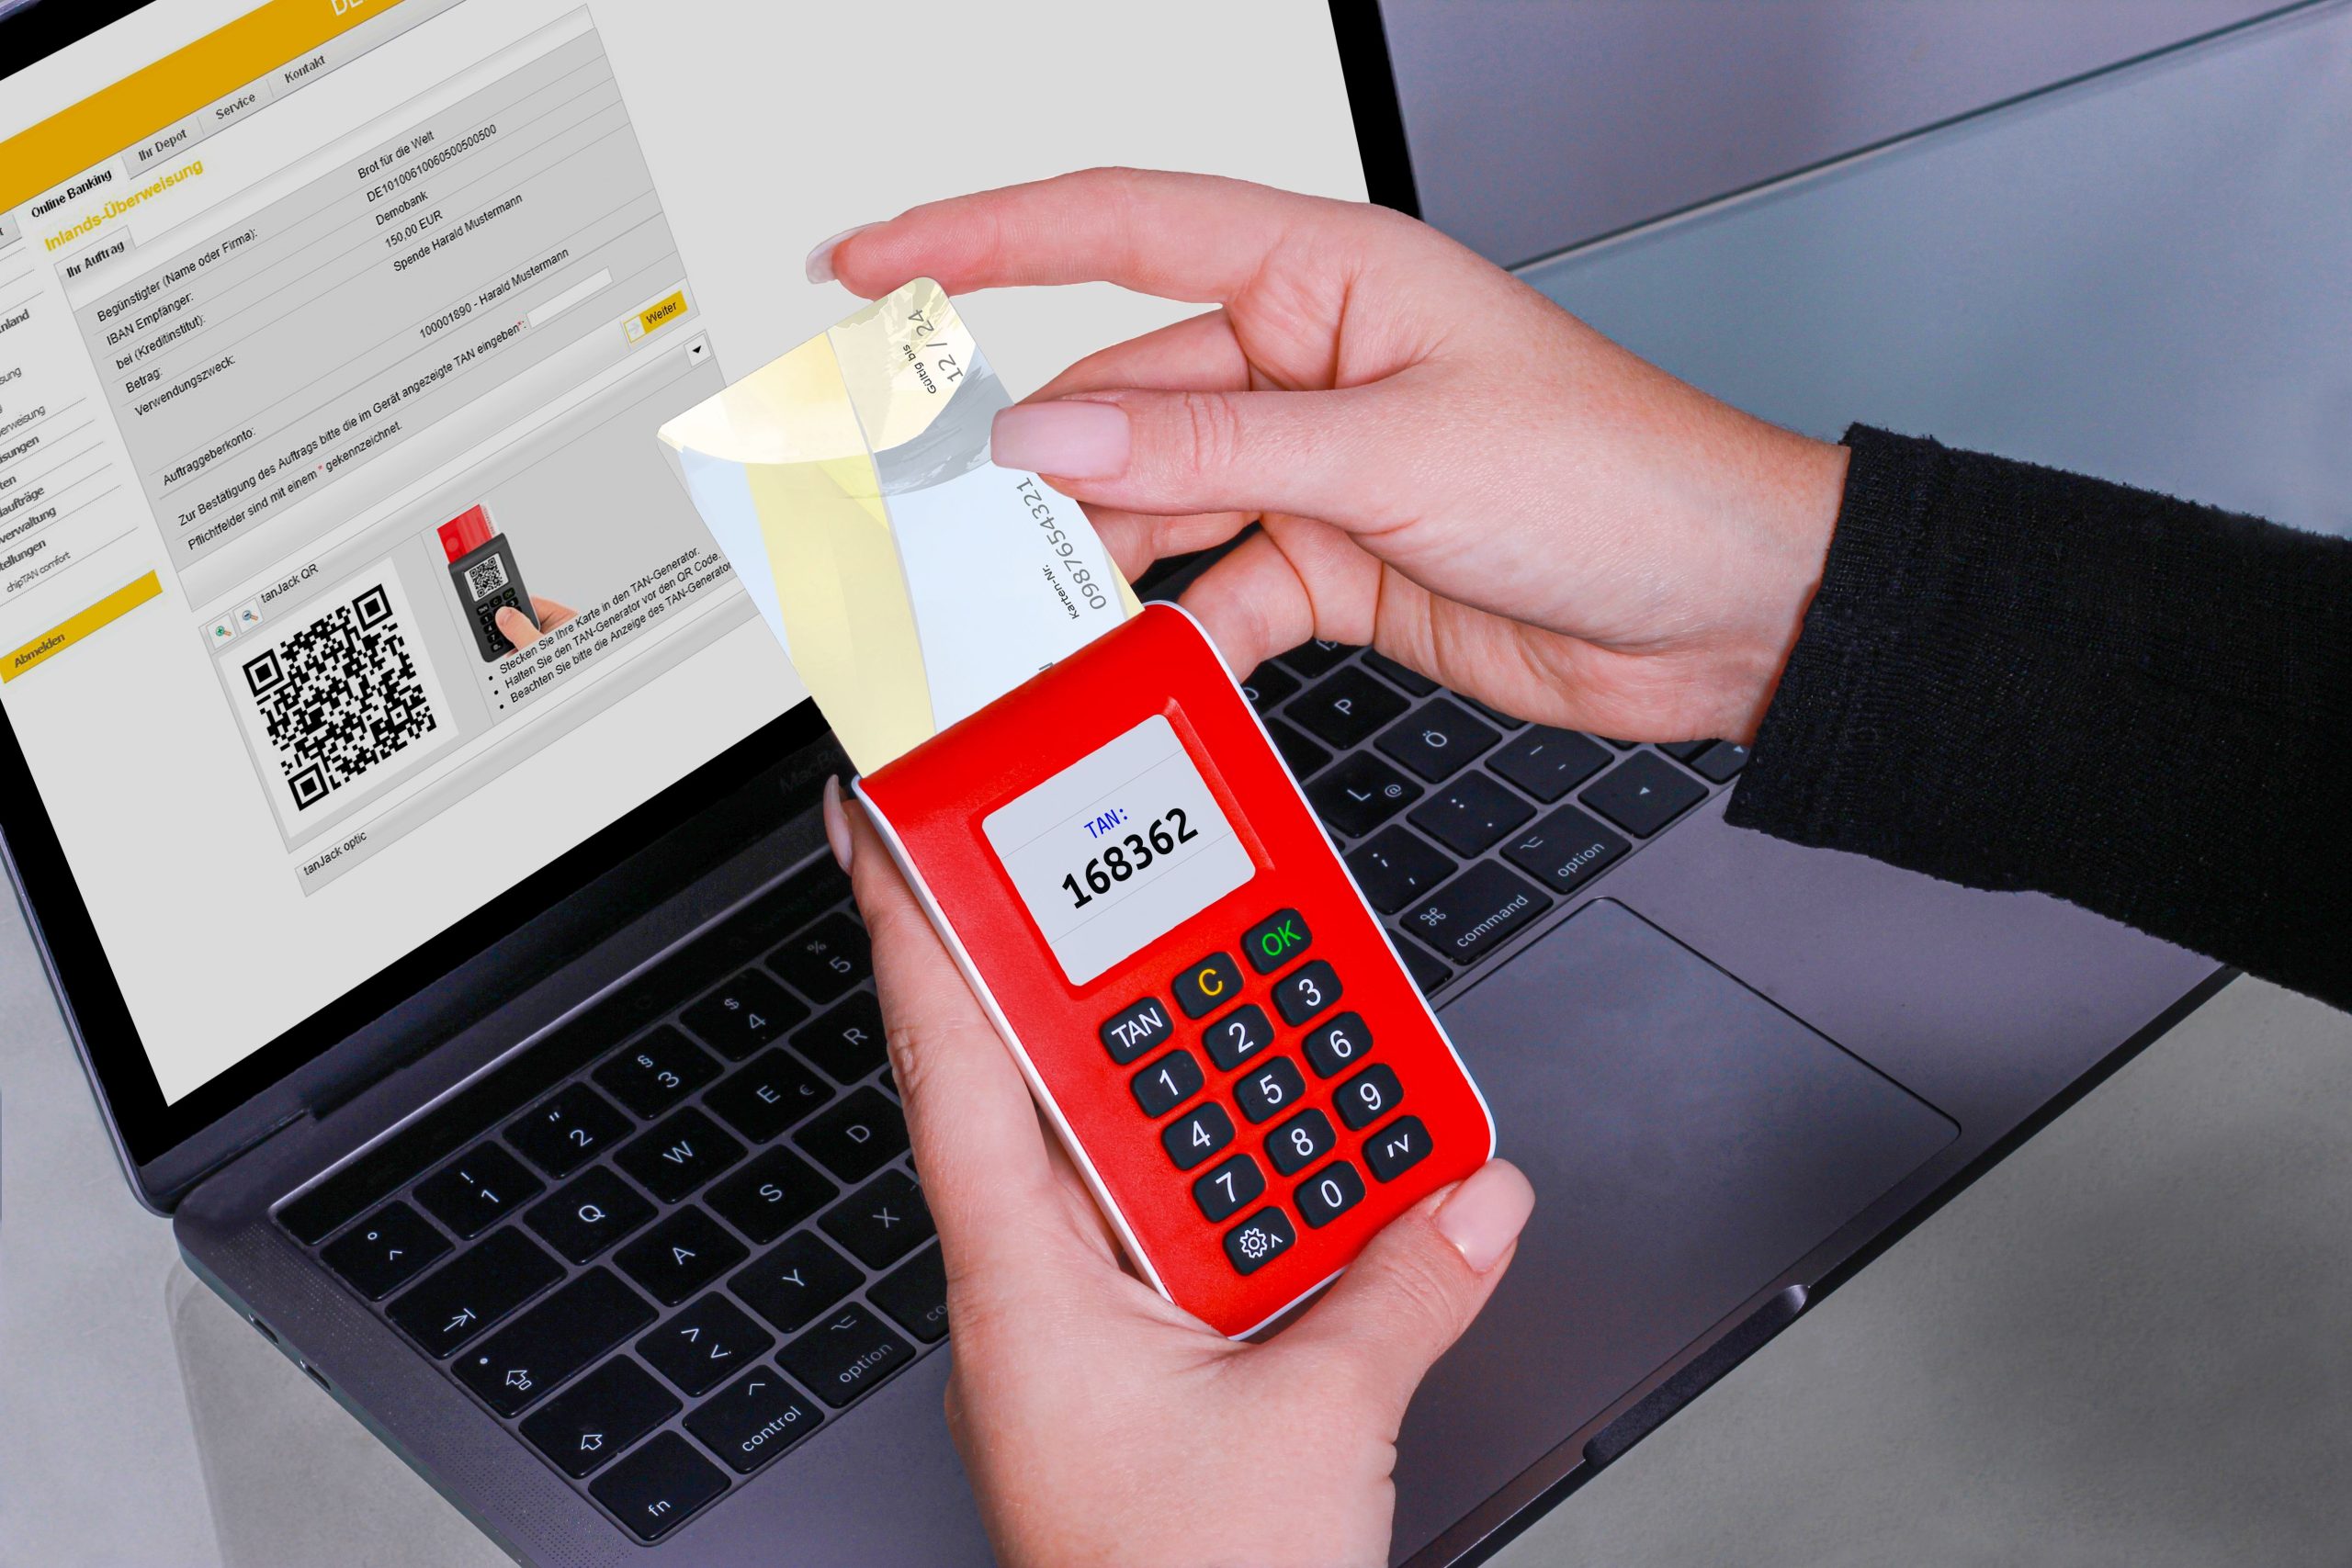
- Something you have: A smartphone, security token, or hardware key.
- Something you are: Biometrics such as fingerprint or facial recognition.
Typically, 2FA prompts users to provide two different categories of data, making unauthorized access significantly more challenging.
Two-Step Verification (2SV)
Two-step verification also entails two separate steps during the login process. Though labeled differently, it generally involves:
- Entering your password (first step).
- Providing a second form of authentication, such as a code sent via SMS, email, or generated by an authenticator app (second step).
In most cases, 2SV is implemented as a process with two distinct phases or steps to confirm your identity, even if the methods used in each step may be similar to those in 2FA.
Are They Technically Different?
The distinction between 2FA and 2SV often lies more in terminology and context than in fundamental technical differences. Many experts and security professionals consider 2FA as a specific subset of 2SV—where two factors from different categories are used for authentication. Conversely, 2SV might refer broadly to any login process requiring two steps, regardless of the factors involved.
For example, if a service asks for a password and then a code sent via SMS, this could be described as 2SV. If it also verifies using a hardware token and biometrics, that system exemplifies 2FA with multiple factors.
Practical Implications
From a security perspective, the most important aspect is the strength and variety of factors used, rather than the specific terminology. Using multiple factors from different categories (e.g., password + hardware token) enhances security more than merely going through two steps with similar methods.
Choosing the Right Security Measure
When updating your account security:
- Prefer services that support true two-factor authentication, especially using hardware keys or biometric factors.
- Be aware that two-step verification methods like SMS codes still significantly improve security, but might be vulnerable to certain attacks like SIM swapping.
- Always enable multi-factor options wherever available, and understand the specific factors involved.
Conclusion
While “two-factor authentication” and “two-step verification” are often used interchangeably in everyday conversation, they can have subtle distinctions rooted in their technical implementation. Ultimately, both mechanisms serve to strengthen your online security by requiring multiple forms of verification. The key takeaway is to utilize these security features effectively, understanding their methods and limitations to better protect your digital life.
Stay informed about cybersecurity best practices to keep your accounts safe and secure.